Do eQSLs need Digital Signatures and Public Keys?
by Dave Morris, N5UP, Founder and Webmaster, eQSL.cc
March 15, 2001
(This topic has the potential to make your eyes glaze over, but I'll try to keep you awake!)
There has been quite a bit of discussion and confusion about whether or not eQSLs are secure, and whether or not
someone needs to add encryption or digital signatures or public keys or some other kind of security to them.
Unless you are familiar with these technologies, it can seem overwhelming.
Let's start with a comparison of 2 very different concepts of how to handle eQSLs.
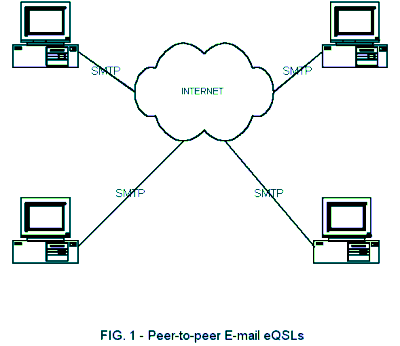
Figure 1 illustrates one method, which I call "Peer-to-peer E-mail eQSLs".
You can find a sprinkling of web sites that promote this type of eQSL, but you will never find more than a handful of
people using them. Why? That will become immediately apparent when you study the diagram, because there is no one
organization with a vested interest in accumulating a large user base.
Notice that each ham must create his own QSL card design using any software package he wants to.
He then looks up the e-mail address of each ham he wants to send a card to, and e-mails the QSL out.
Some form of authentication is required to make sure that when an e-mail arrives saying it is from
JohnSmith@hotmail.com, that we can verify that the sender really was JohnSmith@hotmail.com,
and not some hacker who is generating bogus e-mails. For instance, that function could be performed by
a worldwide digital signature server such as is available through ZixMail.
However, you still do not know that JohnSmith@hotmail.com is really John Smith, the licensed amateur radio operator.
Problems:
- You have to look up every e-mail address before you can send the QSL card;
- Recipients have to figure out how to store each and every QSL card they receive in e-mail;
- Since each sender makes up his own cards using whatever graphics technology he wants to, if there are problems
displaying or printing the cards, the recipient has to work the problems out with each and every sender individually;
- After the card has been printed, it loses its ability to be verified - thus, anybody with a copier and an eraser
can change the card, and nobody can verify its authenticity;
- If you implement a system that allows authentication for an indefinite period of time after receipt, then
you have to purchase and install special software to do that;
- Somebody still has to authenticate that each person who sends an e-mail is the authorized holder of that licensed callsign;
- Every user of the system must learn how to use PGP or ZixMail or some other public key system.
These are either so complicated to use that nobody uses them (PGP), or they cost money (ZixMail).
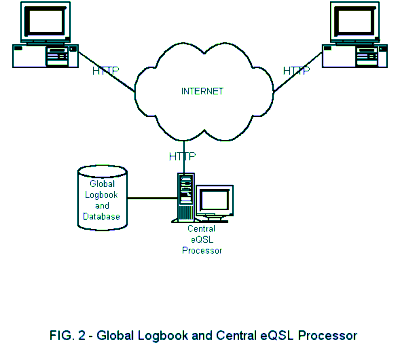
Figure 2 illustrates the patent-pending method used at eQSL.cc which I call a "Global Logbook and Central eQSL Processor".
It is a centralized system where all of the computing power is stored at the center, and the users
have thin clients (browsers) with which they create, post, and retrieve their cards when they wish to display or print them.
In this configuration, nobody has to look up any e-mail addresses. Nobody has to purchase graphics software.
Nobody has to purchase or learn how to use cryptographic software.
Through a series of different security measures, the Central Processor determines and guarantees that a particular user
is in fact the license-holder of a particular callsign, and uses common "UserID and Password" techniques to maintain
the integrity of that guarantee.
Advantages:
- Cards can be verified even after printing by looking them up in the Global Logbook;
- E-mail addresses come and go, but the users do not need to keep up with them;
- All graphics are produced using common technology, assuring that the widest possible viewership can display and print them;
- Users do not need to purchase graphics software;
- Users do not need to install any special software other than a browser;
- Users do not need to learn how to use digital signatures, public keys, or cryptographic software;
- Ham organizations can create their own awards programs and contests, and can use the Global Logbook to verify
QSOs instead of having to handle paper QSL cards in the mail;
- Users have a single point of contact to resolve any problems in making eQSLs work;
While the Peer-to-Peer E-Mail eQSL concept has been tried in the past, it simply poses too many obstacles to widespread use.
It is more complicated, less organized, and eQSLs cannot be validated after they have been printed.
We believe it is for this reason that eQSL.cc has received the huge groundswell of support, with the total card count
in our database doubling roughly every 6 weeks.
So, do eQSLs need digital signatures and public keys? The answer is, if one uses our eQSL system, no!
The security is already implemented in a combination of inspection of license images, UserID/Password security, and
after-printing verification against our database. Anything else just adds complexity for no apparent benefit.
Permission granted to reprint this article in whole or in part.
Please send an e-mail to Support1@eqsl.cc to notify us if you do so.
|